Related Topics:
Scaffold Scaffolding Engineered Access-
What is the terminal access switch port
A console port in a network switch is a dedicated physical interface that allows administrators to directly connect a computer or terminal to the switch for configuration and management. The cable you use depends on the type of Supervisor Engine and other factors. Administrators can remotely control numerous network devices from a single point of access by using a console server, a device that combines several serial. An access port connects an end device like a PC or printer to one VLAN on a Cisco switch. Then you assign a VLAN ID with "switchport access vlan" plus the number. If a switch port is operating in “access” mode, it can be assigned to only a single VLAN, adding additional security.
[PDF Version]
-
Moldova loses internet access
Key Insight: Moldova has made significant progress in expanding internet coverage, with an overall penetration rate of 78% in 2026. Moldova's internet is relatively free, though the government has imposed some limitations in recent years, particularly during states of emergency. The overall infrastructure is well developed which allows many users. Discover population, economy, health, and more with the most comprehensive global statistics at your fingertips. If you want to check whether this is our most up-to-date report for Moldova, or if you're looking for data on digital trends and behaviours in.
[PDF Version]
-
Access Control for Network Security Devices
NAC, meaning Network Access Control, is an advanced cybersecurity measure regulating which entities gain access to which specific network resources. Beyond traditional security parameters, NAC enforces specific access policies, ensuring only compliant devices and authorized users. Network access control, or NAC, solutions support network visibility and access management through policy enforcement on devices and users of corporate networks. Identifies devices attempting to connect. Policies may be based on authentication, endpoint configuration. Upgrading from password- to certificate-based authentication with a Public Key Infrastructure (PKI) significantly strengthens NAC frameworks.
[PDF Version]
FAQs about Access Control for Network Security Devices
What is network access control (NAC)?
Network access control (NAC) is the process of restricting unauthorized users and devices from gaining access to a corporate or private network.
What are the advantages of network access control?
Network access control comes with a number of benefits for organizations:Control the users entering the corporate networkControl access to the appl...
What is the importance of network access control?
Network access control helps in many areas, but specifically provides: Improved Security, Saves Costs, Automation, Enhanced IT Experiences, and Eas...
-
Telnet access to the access switch
In order to remotely access the CLI of your switch, you must use an SSH or Telnet client. Accessing the CLI allows commands to be entered in a terminal-based window. They are the widely used local switch console port login, the remote login by. By default, Telnet services are enabled on the switch and all virtual routers listen for incoming Telnet requests. The switch accepts IPv6 connections.
[PDF Version]
-
Switch Access Port Restrictions
In this lesson, you will learn how to configure port security to restrict the number of MAC addresses per port, specify which MAC addresses are allowed, and control what happens when violations occur. To understand port security, you should be familiar with how switches learn MAC. Port security is an essential security feature on switches. This tutorial explained the commands and configuration steps you need to secure switch ports. If a device connects and its MAC is allowed, all good. With this mechanism, a specific port of a switch can be protected with undesirable access.
[PDF Version]
-
Passive Fiber Optic User Access Equipment and Routers
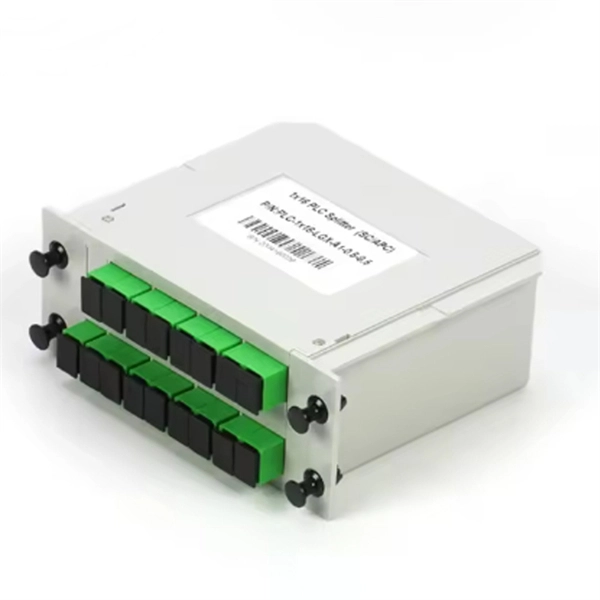
A passive optical network (PON) is a fiber-optic telecommunications network that uses only unpowered devices to carry signals, as opposed to electronic equipment. In practice, PONs are typically used for the last mile between Internet service providers (ISP) and their customers. In this use, a PON has a point-to-multipoint topology in which an ISP uses a single device to serve many end-us. Components and characteristicsA passive optical network consists of an (OLT) at the service provider's central office (hub), passive (non-power-consuming) optical splitters, and a number of (ONUs) or Passive optical networks were first proposed by in 1987. Two major standard groups, the (IEEE) and the. A PON takes advantage of (WDM), using one wavelength for downstream traffic and another for upstream traffic on a (ITU-T, typically OS2). BPON, EP.
[PDF Version]
-
User authentication by access layer switches
A Network Authentication Protocol is a security mechanism implemented at the network access layer. When a terminal device (like a computer, printer, or smartphone) tries to connect to a switch and access network resources, this protocol ensures the user or device is authenticated. Network authentication protocols address this by managing access, enforcing dynamic policies, and integrating with tools like firewalls, NAC, and zero-trust frameworks to enhance security and control. Read this topic for more information. Unless otherwise noted, the term switch refers to a standalone switch or a switch stack. The following restrictions. Cisco Meraki MS switches offer the ability to configure access policies, which require connecting devices to authenticate against a RADIUS server before they are granted network access.
[PDF Version]
-
Core Aggregation Access Switch
As the aggregation point of access switches, the aggregation switch is required with the ability to process the access layer information and submits it to the upstream chain of the core layer. And it needs the function of network isolation and segmentation as well. Function: Connection point for all devices on a segment of segment of a network that breaks down and absorbs the data flow between all of the connected devices rather than flooding it to all connected devices. Fault Tolerance and High. They support link aggregation protocols such as Link Aggregation Control Protocol(LACP) and Static Link Aggregation, which allow multiple physical links to be combined into a single logical connection. This enhances bandwidth, redundancy, and ensures failover capability in case of a link failure. The multi-tier design model supports many web service architectures, including those based on Microsoft. NET and Java 2 Enterprise Edition. High Port Density: Offers 24 to 48 ports per unit, ideal for device-heavy office floors.
[PDF Version]
-
How to access CAD cable trays
In File > Environment > Systems and Lines, you can manage the Cable Tray lines as well as the Systems that these lines belong to. In the Electrical workspace, click Home tabBuild panel. Find For the remaining steps, use the Properties palette for conduit settings or the Add Cable Trays dialog box for cable tray settings, as shown next. The cable tray and conduit tools have specific. You can perform the following to route cable trays in the 3D model. Create a new project. Learn how to draw pipe and duct networks, connect components, generate schemes, and create slots and openings. Explains the concept of. Discover all CAD files of the "Cable trays" category from Supplier-Certified Catalogs ✅ SOLIDWORKS, Inventor, Creo, CATIA, Solid Edge, autoCAD, Revit and many more CAD software but also as STEP, STL, IGES, STL, DWG, DXF and more neutral CAD formats.
[PDF Version]
-
EPON Optical Cable Access
EPON means Ethernet Passive Optical Network. These cables give fast and steady internet to homes and businesses. Many users can connect with fewer cables. There is no need for. A passive optical network (PON) is a fiber-optic telecommunications network that uses only unpowered devices to carry signals, as opposed to electronic equipment. This prevents electromagnetic interference from external devices and lightning. An EPON (Ethernet Passive Optical Network) module is a key component in fiber optic networks designed for high-speed data transmission. EPON modules are integral to the EPON architecture, facilitating the seamless exchange of data between network components such as Optical Line Terminals (OLTs) and.
[PDF Version]
-
The access switch is constantly changing its topology
To fix frequent STP topology changes, you should start by using the 'show spanning-tree' command to identify any problematic ports. Then, check the physical connections to ensure there are no faults and that everything is stable. I've already checked and confirmed that “spanning-tree portfast edge” and “spanning-tree bpduguard enable” are configured on all access switches. Has anyone dealt with this issue. Hello, recently we have recieved some topology change messages on our core switch (5900 IRF stack, stp. Logbuffer: MSTP/6/MSTP_NOTIFIED_TC: Instance 0's port Bridge-Aggregation1. The switches are connected through fiber cables. We found one switch having multiple. The issue isn't causing any major disruptions, but it is concerning. RSTP runs on switches by default, and we do not explicitly configure the core switch as the root bridge for all VLAN as we think. I am working with support on an issue where randomly we have a network interruption that looks like it's caused by some aggregate ports on our MS425 going down and back up and causing spanning tree topology change. Anyway, looking in the event log I see this a.
[PDF Version]
-
Eor access switch
An EoR (End-of-Row) switch is a network switch placed at the end of a data-center rack row, aggregating connections from multiple server racks into a centralized switching point. All servers in the row connect to the EoR switch using structured horizontal cabling, typically copper. In contrast to the TOR architecture, EOR architecture provides unified network access points at the end of each row of cabinets. Datacenter architecture design is largely dependent on data communication and the interconnection of switches. When there are a lot of servers to connect (like in a Data Center), networking needs to be flexible/scalable enough to handle the computing power required for large installations.
[PDF Version]
-
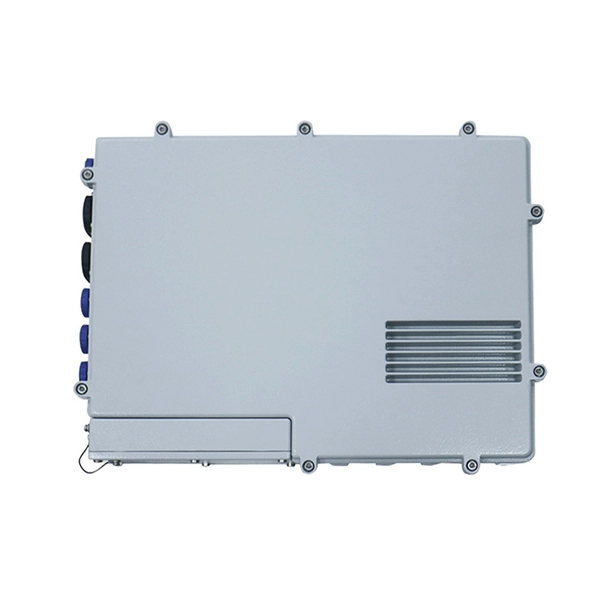
The methods for using fiber optic access switches include
Control signal choices for fiber optic switches include RJ-45, RS232, RS422, and TTL. Common switch features include rack mountable and LED indicators. An important environmental parameter to consider for fiber optic switches i. Control signal choices for fiber optic switches include RJ-45, RS232, RS422, and TTL. Common switch features include rack mountable and LED indicators. An important environmental parameter to consider for fiber optic switches is the operating temperature.Fiber optic switches can interface with two types of cables: 1. single mode 2. multimode Single modeis an optical fiber that will allow only one mode to propagate. The fiber has a very small core diameter of approximately 8 µm. It permits signal transmission at extremely high bandwidth and allows very long transmission distances. Multimodedescribes. Important switch performance parameters to consider when searching for fiber optic switches include: 1. wavelength range 2. number of input ports 3. number of output ports 4. switching time 5. insertion loss 6. polarization dependent loss 7. cross-talk 8. data rate 9. switching voltage The wavelength range specifies the wavelength range the switch.
[PDF Version]